Approvals you can explain later
Oprivia brings requirements, submitted evidence, and review decisions together. Authorized people review the outcome and decide whether to approve it or request rework. The record shows who reviewed the work and why the case was closed.
Professional responsibility remains with the accommodation operator
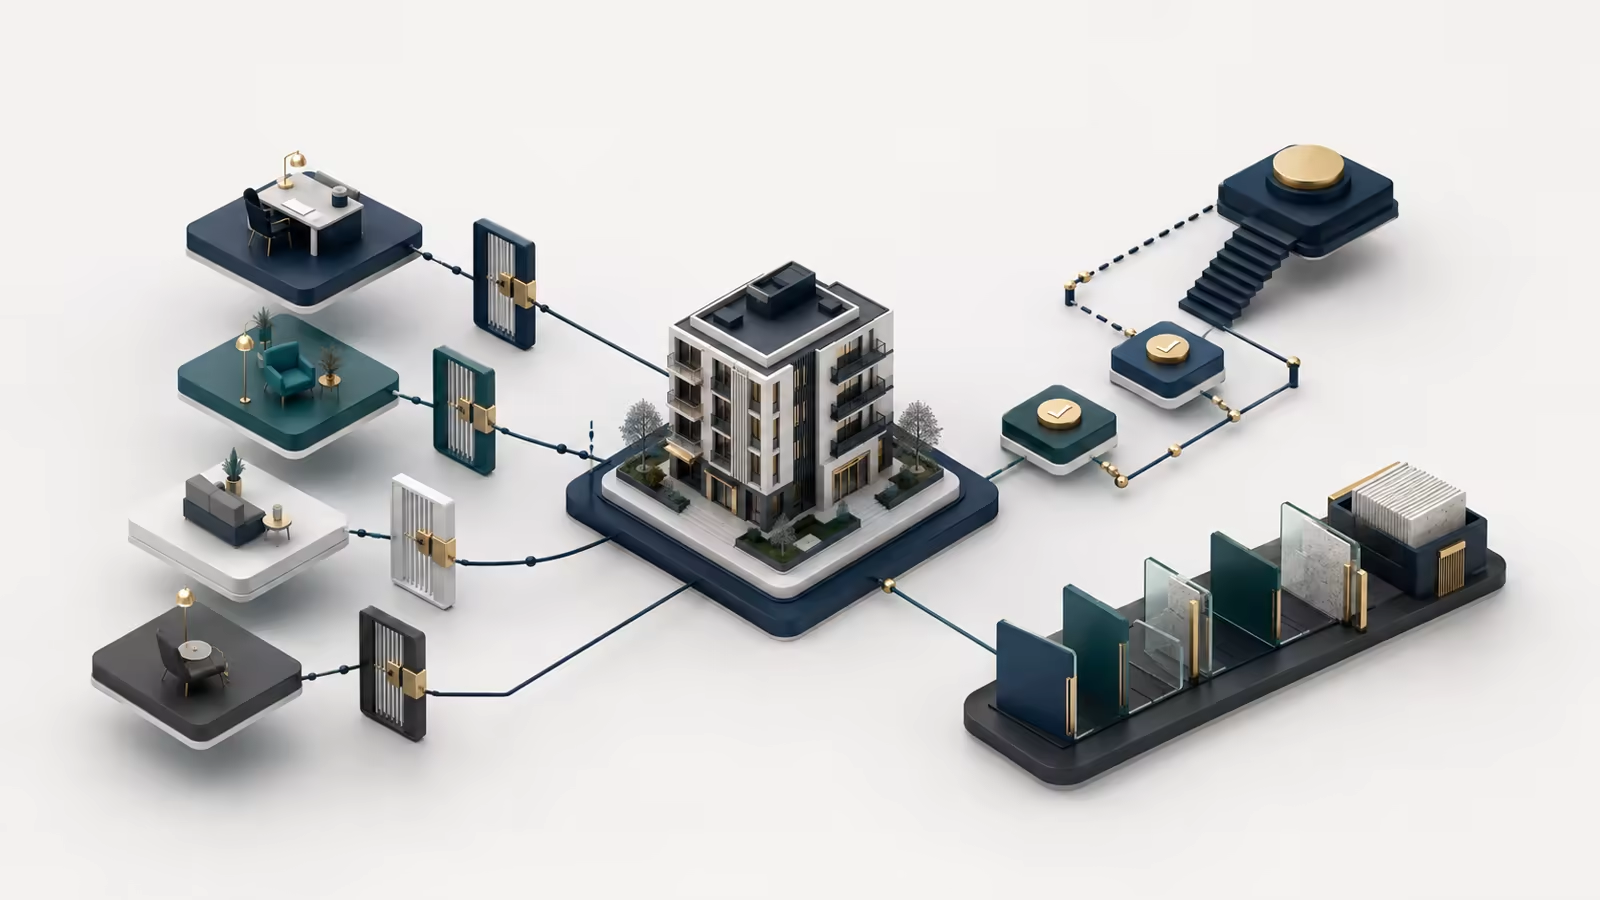
Oprivia makes requirements, review points, and decisions traceable. Selecting the applicable rules, interpreting them professionally, and approving a specific course of action remain the responsibility of the accommodation operator and its qualified advisers.
Ownership and access
Roles, permissions and visibility are limited to the assigned area of responsibility.
Status, deadlines, and follow-up
Open items, time windows, and approaching or missed deadlines make required action visible.
Checklists and evidence
Checklists, feedback, documents and photos remain linked to the relevant case.
Escalation and decision
Unresolved matters are routed to the accountable role through defined paths.
Continuous audit trail
Updates extend the record without overwriting earlier workflow states.
Service boundaries
The platform supports control and documentation, but does not replace legal or regulatory assessment.
Four roles, clear boundaries
Oprivia provides the governance layer for operational workflows after a booking has been confirmed. Guest, Host, Operator, and Administrator/Governance each receive a separate view and scope of action. This makes it clear who provides data, completes work, reviews exceptions, and controls rules or approvals. Permissions that are not assigned remain blocked.
Guest
Guests see only information about their own stay, provide required details and documents, and manage their own service requests.
Host
Hosts manage their own properties or portfolio, assign Operators, and see relevant operational and compliance information.
Operator
Operators complete assigned tasks, work through checklists, and add photos or other evidence. Rule configuration and governance decisions remain outside this role.
Administrator and Governance
This role manages rules and permissions, reviews escalations and sensitive cases, and controls the audit trail. Operational service work is outside its scope.
Resolve exceptions clearly
An open item is linked to the relevant case, assigned to an accountable role, reviewed through a defined process, and closed with a documented outcome.
Case context
Case context
Link the open item
A request, task, or deviation is linked to the relevant stay, property, or assignment.

Role ownership
Role ownership
Assign accountability
An accountable role, current status, and, where required, a time window determine the next step.

Evidence trail
Evidence trail
Document the work
Checklists, feedback, documents, and photos are linked directly to the relevant case.

Escalation logic
Escalation logic
Route the exception
Missing information, overdue items, or unresolved matters are routed to the accountable role.

Approval gate
Approval gate
Record the decision
The decision, rationale, and person who acted are documented. The preceding case history remains intact.

Changes extend the audit trail
Case status, checklists, photos, documents and approvals remain linked to the relevant case over time.
New information extends the record instead of hiding earlier states. Critical decisions are made by accountable people, not by the system.
- Timestamps and accountable roles remain visible.
- Records and decisions remain preserved in the case history.
- Corrections are added, not hidden retrospectively.

Control how rules are activated and changed
Governance does not end with the initial configuration. New roles, changed deadlines, or additional automations are reviewed before activation, assigned to an accountable role, and documented.
Status changes, reminders, assignments, and escalations can be triggered by defined rules within the agreed operating scope. Approvals, sensitive outcomes, and material decisions remain with the designated people.
Record the change request
The reason, affected workflow, intended effect, and accountable role are documented.
Assess the impact
Access, data processing, deadlines, evidence requirements, and existing rules are checked for conflicts before the change.
Approve and test the change
Authorized people review the adjustment. Critical changes are first tested within a limited scope.
Document the version and outcome
Activation time, approval, affected rules, and later corrections remain traceable.
Control strengthens accountability; it does not replace it
Personal data is processed for the relevant operational purpose. Visibility depends on roles, tasks and agreed access rights. Oprivia does not replace official filing, registry, or regulatory portals. Where an integration has been expressly agreed and is available, the platform may support submission; the official confirmation or decision remains with the competent authority. Feature availability depends on the current release, the scope agreed in writing, and the active configuration. Oprivia supports process control and documentation, but does not replace legal, data protection or regulatory assessment.
Process only required data
Only data required for the relevant purpose is processed. Access depends on role and task. Retention and deletion follow the agreed or legally required rules.
No transfer of legal responsibility
Oprivia does not provide legal, data protection or compliance advice, regulatory certification or expert case-by-case assessment.
Configure governance for your operation
During setup, we define roles, access, checkpoints, time windows, and escalation paths for your operation. Onboarding supports regular use within the agreed scope. If you want to assess a workflow under limited conditions first, we can agree on a pilot.