An audit trail is a chronological history tied to a particular case. It shows what happened, who acted, what supported a decision, and whether an earlier record was later changed. It improves reviewability, but it does not make the underlying claim true or establish legal evidentiary weight.
A single misunderstanding can often be cleared up with a phone call. Across multiple properties, shifts, and outside partners, memory is no longer enough. Decisions need traceable context, whether they concern a cleaning release, guest complaints and refund claims, or property damage.
What an audit trail must answer
The record must connect each decision to the evidence available at the time.
These concepts are related but distinct. Evidence supports an assertion. A log entry records an action or state. The case chronology connects both with the accommodation, stay, assignment, and decision. The combined history should explain the operational outcome: Why was the unit released, rework ordered, or a claim submitted?
Define the evidence requirement before taking the photo
Many operators start with the camera and wait until a dispute to ask what the image was supposed to show. Reverse that order. First identify the decision that may later need explanation. Then specify the information and evidence needed to support it.
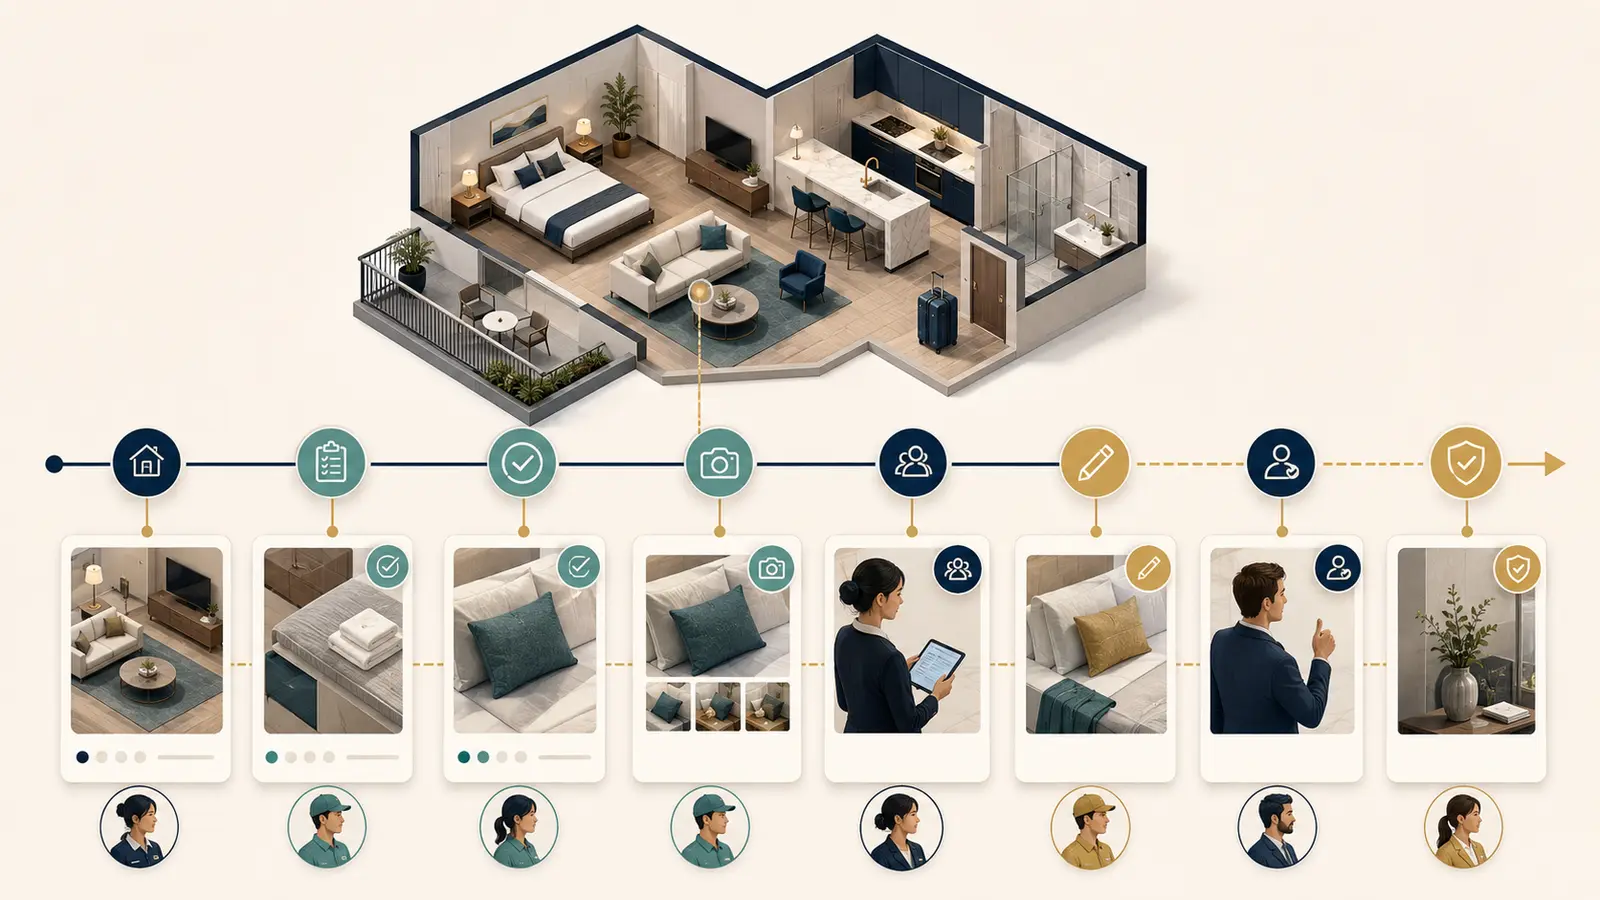
For a cleaning release, the chain might look like this:
- Case context: The accommodation, area, stay or turnover, and assigned job are unambiguous.
- Requirement: The checklist describes the expected condition, not merely the activity.
- Capture: The photo shows the required area at usable quality.
- Source: The role that captured it and the submission channel remain identifiable.
- Time context: Capture, upload, and review times are shown separately.
- Review: An authorized person accepts the evidence or requests rework.
- Correction: Incorrect evidence is marked and supplemented with a new item, not silently overwritten.
- Closure: The decision, rationale, and any unresolved issues are recorded in the case.
This structure is leaner than requiring a photo of every action. It follows the purpose. A key handoff needs different evidence from a damaged countertop. Collecting everything does not automatically create more certainty. It often creates opaque data collections and additional privacy risk.
Time, source, and version belong together
A single timestamp is less definitive than it appears. A camera may store a capture time, a platform may record an upload time, and a system may add a server time. With a poor connection, hours can separate them. Reviewers therefore need to know which time each timestamp represents.
Metadata embedded in an image is useful only to a point. It can disappear during export, editing, or transmission, and it is not immutable. A stronger approach does not rest on one attribute. The original file, submission path, case association, and recorded review work together.
If a photo is cropped or reduced for a report, retain the original and identify the derived version as such. A cryptographic hash can also indicate whether two digital files are identical. It does not confirm the capture location, authorship, or truth of the content. That boundary matters: technical integrity and factual truth are not the same.
Corrections and handoffs must not erase the history
A user account is not conclusive proof of the individual who acted. Authentication, sessions, roles, and device security all affect attribution. Read, export, and administrative rights for sensitive logs should be limited; access should be logged; backup and restoration should be tested; and unauthorized changes should be detectable. ISO 15489, ISO 23081, and NIST SP 800-92 provide guidance, but they establish neither certification nor technical immutability.
A kitchen photo assigned to the wrong case should not be replaced without explanation. The cleaner or reviewer marks the error, records the reason, and adds the correct evidence. The earlier entry remains visible to authorized roles. A later reviewer can then tell whether the property was released without review or the error was caught and corrected in time.
The same principle applies to status changes. “Completed” records the service provider's report. “Reviewed” records the control step. “Released” records the operational decision. Combining those states erases a critical handoff. The guide to controlling cleaning quality in short-term rentals shows how to apply this separation during turnover.
Roles and access rights are also part of the evidence chain. The person doing the work may capture evidence for the assigned job. A responsible manager reviews or rejects it. Administrative roles manage rules and access, but they cannot overwrite historical events or alter evidence. Appropriate rights depend on the task, risk, and type of data. The article on Roles and Access Rights in Vacation Rentals explains this in more detail.
A reviewable export explains the case
A ZIP file containing one hundred images is not yet an understandable case file. A useful export arranges the relevant elements in a readable chronology. It includes the case identifier, accommodation, relevant period, roles, events, status changes, rationales, and references to the associated original files. Corrections appear as new steps.
Example: Correcting a Kitchen Photo Assigned to the Wrong Unit
This editorial example shows what a traceable chronology should connect. It is not an extract from a customer record.
- Submission: The cleaner attaches a kitchen photo to the work order for Unit A and reports the work complete.
- Review: The reviewer notices that the photo shows Unit B, records the mismatch, and requests the correct evidence.
- Correction: The cleaner adds the right photo. Authorized users can still identify the incorrect item and the reason for the correction.
- Decision: The reviewer assesses the new evidence and records whether the release requirements are met or something remains outstanding.
A later reader must be able to identify the evidence available for each decision. The corrected photo alone does not explain the original error or the review that followed.
A second review is necessary before sending it. Does the export contain only information needed for the recipient and purpose? Does it include guest information or internal notes that should be redacted or omitted? Is it clear whether timestamps use local time or Coordinated Universal Time? Are original files retained internally when only copies are used for communication?
Such a file can help with an internal root-cause review, a discussion with a service partner, or preparation for a platform or insurance inquiry. It does not decide the case. Insurers, platforms, authorities, and courts assess the materials under their own rules.
Evidence law and data protection ask different questions
Under the Swiss Civil Procedure Code, electronic files can qualify as documentary evidence if they are capable of proving legally relevant facts. Courts assess evidence freely. If the opposing party challenges a document’s authenticity on sufficiently substantiated grounds, the party relying on that document must prove its authenticity. This offers operators no guarantee, but it does suggest a practical lesson: context, source, and visible corrections may matter more to a later assessment than the sheer number of files.
Data protection law applies a different test. Personal data must be processed lawfully, proportionately, for a defined purpose, and with appropriate security. Logging under Article 4 of the Swiss Data Protection Ordinance applies to private controllers only under specified conditions. It is not a blanket requirement for every vacation rental or every workflow. Where processing falls within its scope and preventive measures are insufficient, the ordinance identifies operations to be logged and requires those logs to be retained separately for at least one year. The guidance from the Swiss Federal Data Protection and Information Commissioner also explains that such logs should not be used to monitor behavior.
An operator should therefore document which data it collects and why, who may access it, how long it is needed, and how deletion or restriction will occur. Professional data protection review is prudent for sensitive or extensive processing.
Common questions about audit trails
Does a timestamp prove when and where a photo was taken?
No. Capture, upload, and server times are useful signals, but they can differ. Place and time require additional case context.
Is a screenshot from a messaging app enough?
It may support an assertion, but it often omits the complete thread, time zone, or later changes. Depending on its significance, retain the original thread or export and add a case-linked note.
Can an incorrect entry be deleted?
A material error should be corrected visibly so the chronology remains understandable. That does not justify unlimited retention. Requirements for correction, purpose limitation, access restriction, and deletion still need to be assessed for the specific record.
Is Oprivia’s audit trail tamper-evident?
The functional specification defines critical audit events as immutable and append-only. Administrators cannot overwrite or delete historical events or alter evidence. Whether these controls are available in a particular deployment depends on the approved product release. Even when active, they do not prove the truth or authenticity of an uploaded file, make the entire case record tamper-proof for every purpose, or determine legal evidentiary weight. An electronic signature is a separate mechanism and is not equivalent to a simple timestamp.
Can Oprivia detect and escalate overdue services automatically?
Partly. Within the agreed deployment scope, Oprivia can keep a work order’s deadline, acceptance, and status together and use configured SLA thresholds to show an approaching or missed deadline. Countdowns, at-risk indicators, reminders, and breach logging are provided for in the functional specification; their availability depends on the approved release, contract, and configuration. Automatic escalation of every overdue service is not promised. Critical breaches can be handled as governance escalation cases, while emergencies follow the on-call protocol.
Does the history guarantee acceptance by a platform or insurer?
No. It improves traceability and plausibility. The recipient independently assesses deadlines, relevance, and authenticity under its own terms.
Oprivia connects the case, but does not decide it
Oprivia is available for customer use as a post-booking operational governance layer. Within the approved scope, tasks, roles, statuses, evidence, reviews, and escalations can share one case context. Available capabilities depend on the release, module, contract, and configuration. Oprivia does not confirm evidence authenticity, determine liability, or assign legal evidentiary weight.
The full post-booking operations guide shows where this evidence is created across the wider workflow.
Before rollout, model one real workflow from beginning to end, such as turnover after a departure. This short review is enough to start:
- Which decision may need to be explained later?
- Which three to five pieces of evidence are actually needed?
- Who captures, who reviews, and who releases?
- Which timestamps must remain separately visible?
- How are errors corrected without obscuring the prior record?
- Which data belongs in an export, and which data is expressly excluded?
- When are evidence and logs deleted or restricted?
A record is reliable when a third party can follow the path from requirement through performance to decision; collecting more images does not achieve that by itself.
Sources and Notes
Editorial and professional context
Sources reviewed: September 10, 2026. The review included current Swiss legislation, guidance from the Swiss Federal Data Protection and Information Commissioner, and the professional and technical references below. The evidence sequence, distinctions, examples, and checklists are editorial models for operational use. They make no claim about the evidentiary weight of any particular document.
External professional sources
- Swiss Civil Procedure Code, particularly Articles 157, 177, and 178: current provisions on the free assessment of evidence, electronic documents, and disputed authenticity.
- Swiss Federal Act on Data Protection: current statutory provisions governing processing principles and data security.
- Swiss Data Protection Ordinance, particularly Article 4: current rules on conditional logging in automated data processing.
- FDPIC guidance on logging by private controllers, dated September 15, 2023: official guidance on the application of Article 4 of the Data Protection Ordinance.
- FDPIC guide to technical and organizational data protection measures: official guidance on appropriate data security.
- ISO 15489-1:2016, Records Management: an international standard addressing records-management concepts and principles.
- ISO 23081-1:2017, Metadata for Records: an international standard addressing principles for records metadata.
- NIST SP 800-92, Guide to Computer Security Log Management, published in September 2006: technical guidance on log management.
- OWASP Logging Cheat Sheet: actively maintained technical guidance on security logging.
- NIST definition of a hash function: technical terminology used when checking the integrity of digital data.
Oprivia sources
- Oprivia: Post-booking operational platform
- Oprivia: Roles, approvals, escalations, and history
- Oprivia: Modules and operational workflows
- Vacation Rental Damage: Liability, Insurance, and Evidence
- How to Control Cleaning Quality in Short-Term Rentals
Scope and limitations
The material provides general professional guidance rather than legal, data protection, insurance, or evidentiary advice. Logging duties, retention periods, and evidentiary weight depend on the facts, the processing activity, and the applicable law. Oprivia is not an archival service or certification body and gives no assurance that a record will carry a particular evidentiary weight. Product functions vary by release, module, contract, and configuration.