Before the first busy season, an operator brings in extra help. The cleaner receives a spare key, the co-host gets the lockbox code, and a building technician holds an emergency key. Two people share the login for the booking account. When the season and the co-host's engagement end, nobody can say with confidence which copies, codes, and online permissions are still active.
Each shortcut solved an immediate problem. Over time, the shortcuts formed a network of access that no one could see in full. Changing an old code addresses only one part of it. The operator needs to know who may enter a particular accommodation, see particular information, or make a decision, as well as the purpose and duration of that authority.
Physical access and digital access belong in the same control model. A workable model separates personal identity from job role, confines each permission to the relevant property and case, and defines the revocation process at the time access is granted. Technology can enforce parts of that model. It cannot create permission to enter a guest's accommodation or transfer the operator's responsibility to the device.
Begin by listing every key, code, account, and sensitive view
The front door is only one access point. Physical credentials include master keys and copies, lockboxes, electronic locks, parking cards, basement access, and keys to mechanical rooms. Digital credentials reach booking platforms, the PMS, email, cloud storage, electronic locking systems, Wi-Fi administration, and the operational platform. Access to sensitive information must also be counted, including guest records, identity documents, camera footage, and the authority to approve costs or close tasks.
Build the inventory before designing the role matrix. For each credential, record who owns or administers it, who is authorized to use it, why it exists, which properties it covers, when it was issued, how long it should remain valid, and how it will be revoked. For a physical key, record the known number of copies. For an account, identify the users and roles and whether strong authentication is in place. For a code, specify the doors and time periods for which it works.
Example inventory entry: Vendor A; work order 024; unit 12; access during the agreed appointment from 10 to 11 a.m.; approval by the responsible person; deactivate the code after the visit and confirm revocation.
Be honest about uncertainty. If the number of key copies is unknown, enter it as an unresolved gap rather than zero. If several employees share an account, do not attribute it to a fictional single user. An operator can secure or withdraw only the access it knows about. The first corrective steps are therefore quite practical: count the keys, export the user lists, document current codes, and investigate every permission without a clear explanation.
Access depends on the person, role, property, purpose, and time
Identity establishes the person or organization involved. A role describes the work they normally perform. Neither is enough to authorize a particular action. A cleaner may serve two units without being permitted to enter the owner's storage room. A host may manage one portfolio and have no right to view a second company's properties. An administrator may configure accounts without being authorized to approve a repair on technical grounds.
Before allowing access, check each of the following:
- Identity: Which individual or organization will act?
- Role: What task or responsibility does that person normally hold?
- Organization: On whose behalf is the person working?
- Property: Which accommodation, room, or technical area is involved?
- Work case: Which stay, assignment, or service order creates the need?
- Time: When does the permission begin and end, and what access window applies?
- Action: May the person view, change, perform, review, or approve?
The NIST model for Role-Based Access Control assigns users to roles and permissions to those roles. NIST labels the project page as archived and no longer updated. Its core principle remains useful, but accommodation operators also need the property, case, and time context. A role name should never function as a permanent pass.
Three access checks for work order 024
Use the fictional inventory entry for unit 12 to test digital permissions with test accounts. Define what the account may view and do before testing. Then attempt an action that is expressly outside that permission.
- Correct assignment, wrong unit: Vendor A can view the information needed for work order 024 in unit 12 and submit the required evidence. Access to a work order in unit 13 is denied if the account has no permission for it.
- Expired permission: After the defined end time, the same account can no longer open or change the work order covered by that temporary permission. Check this in an existing session as well.
- Changed role: After a role change, the account has the newly defined permissions. Earlier entries remain attributed to the person and role that created them; the change must not alter their recorded origin.
For each check, record the account, organization, work order, permitted and prohibited action, expected and actual result, test time, and software version. A failed check remains an open issue with an owner and correction deadline. Revocation of physical keys or door codes requires a separate check.
Four role families can organize the work
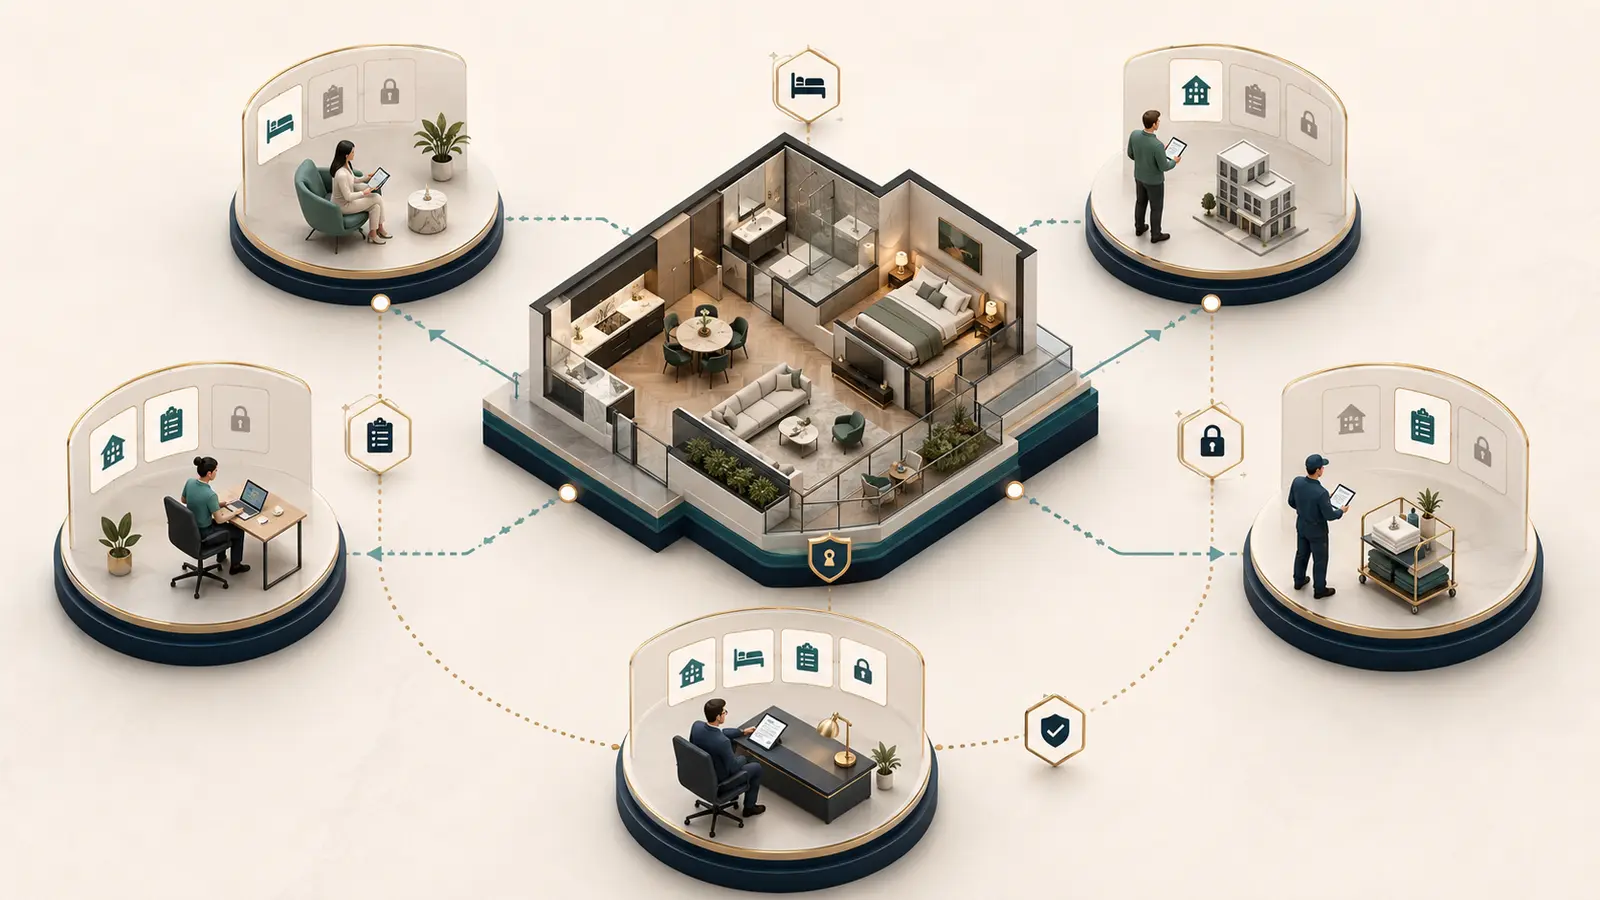
Oprivia describes four work views: Guest, Host, Operator, and Governance. They are families of roles in an operational model, not standard job titles for the accommodation industry. One person may act in different capacities for different organizations or cases. Permissions should follow the work context, not the title alone.
- Guest: The guest sees their own stay, provides required information, and reports requests relating to that stay. Other guests' records and internal control information remain outside the view.
- Host: The host manages assigned accommodations and unresolved matters within the relevant portfolio and coordinates the work. Property ownership by itself does not open every category of sensitive information.
- Operator: The operator performs an assigned job, updates its status, and supplies the required evidence. The work order sets the limits for the property, data, and actions involved.
- Governance: The governance role reviews exceptions, handles escalations, and records approvals or other material decisions. It should not quietly carry out critical work and then approve its own result.
In a small operation, the same person may have to perform several functions. Separation of duties is harder under those conditions, but it can still be applied to the cases that matter most. A costly or sensitive decision may require a second-person check, a recorded review by someone else, or advice from an external professional. The control should be proportionate to the risk.
Vendors particularly need permissions tied to the work case. A plumber does not need general access to the building. The plumber needs entry to a defined area for a named work order and a limited period. The guide to managing vacation rental vendors describes acceptance, entry, evidence, and release for outside work.
Being able to unlock a door is not permission to enter
A guest has a legitimate expectation of privacy during the stay. Airbnb's privacy policy generally requires the guest's permission before a host enters an entire place during a reservation, except in an emergency. The Expedia policy that applies to Vrbo bookings permits entry for an active emergency or for a time-sensitive issue when the guest has given express advance consent. The operator should communicate the reason for entry, its timing, and the expected duration.
For a scheduled vendor visit, the responsible person agrees on a window with the guest, identifies the individual who will enter, and links the consent to the particular stay and work order. Silence should not be interpreted as consent. If an emergency requires entry, limit it to the work that is necessary and record the facts afterward. The contract and applicable law may impose other permissions or restrictions, which require assessment in the individual case.
Ownership, a master key, or an administrator account does not remove these limits. Those things provide the technical means of access. Operators should decide beforehand who can determine that an emergency exists, which attempts to contact the guest are expected, and how a key will be issued. Temporary codes are useful only if their validity is truly restricted by property and time. Without an expiry, a vendor code is a permanent digital key.
Share only the data required for the assignment
The principle of least privilege limits each person's access to what the task requires. A vendor may need the address, a clear description of the problem, the appointment time, and a way to reach the responsible contact. There is usually no reason to send the complete booking history, identity documents, payment information, or private messages from the guest. Among its other requirements, the Swiss Federal Act on Data Protection requires proportionate processing for a defined purpose and appropriate data security.
Shared accounts make this control difficult. When several people use one login, the record cannot reliably show who viewed the data or changed a decision. Individual accounts, appropriate roles, and reliable authentication make it possible to trace an action to the person responsible. These are basic controls, not merely an IT preference.
Cameras and access to recordings require particular care. Airbnb's security camera policy prohibits devices that monitor the interior of a listing, including devices that are switched off. Other platforms and local law may impose their own rules. For private video surveillance in Switzerland, the Swiss Federal Data Protection and Information Commissioner addresses the area recorded, justification, proportionality, transparency, short retention tied to the purpose, and a narrowly limited group of recipients. The guidance indicates that routine viewing is not justified when recordings are needed only to investigate a specific event.
A recording by itself may not establish what caused an event or who is responsible. The Commissioner notes that images can be ambiguous and that a court decides admissibility in the individual case. A damage inquiry therefore needs the surrounding facts. The guide to audit trails for operational evidence explains how source, time, corrections, and decisions can be recorded together.
Design offboarding when the permission is issued
Access moves through a life cycle. Someone requests it, another person reviews and grants it, the user exercises it, and the organization monitors or changes it before eventually revoking it. If the final step is first considered after a person has left, the keys, account details, or administrative rights needed for prompt revocation may already be difficult to find.
At the time access is granted, name the person who will initiate revocation and the person who can carry it out technically. Relevant triggers include the end of a stay, completion of a work order, a change in role, departure from the organization, the end of a contract, loss of a device, and a security incident. Depending on the circumstances, offboarding may require the following actions:
- deactivate individual accounts and terminate active sessions
- review roles, groups, and permissions in connected products
- disable or replace codes and recover keys or access cards
- change any shared password that the operation still uses
- transfer open work orders, files, and responsibility for pending decisions
- record what was completed and identify any gap that remains
The return of a physical key does not establish that no copy exists. If the inventory cannot account for the copies, assess the remaining risk and replace the cylinder or locking plan where necessary. The same problem exists online. Deactivating the main account may leave access through forwarded email, a cloud share, or a vendor portal.
Offboarding follows specific events, but access also needs periodic review. The responsible manager should examine whether the person, role, property, case, and purpose still belong together instead of simply approving a long list of users. The NIST principle of least privilege offers relevant professional guidance, but it does not set a review interval for vacation rental businesses.
Respond to exceptions with a recorded decision
A missing master key, a code used outside its permitted window, a former employee's active account, or an entry that was not coordinated calls for concrete action. Limit the possible access, determine which people or systems may be affected, preserve the available facts, and assign the decision to a responsible role. An escalation remains open until the record states the action taken, its outcome, and any risk that remains.
Fictional example of an administrative change: Partner A can currently work only on work order 024. To cover for another person, the partner needs access to work order 025 in unit 12 until 6 p.m. The authorized decision-maker approves the extension, and an administrator applies it. The change record identifies the previous and new permissions, affected work orders, reason, approver, administrator, and start and end times. After 6 p.m., a check confirms whether access to work order 025 has actually been revoked. Record the time, reviewer, and result. If access remains possible, keep the exception open with a named responsible person until a successful recheck confirms revocation.
In its published model, Oprivia links a stay, case, permission, deadline, evidence, and decision. The role and working context limit access. Guest, Host, Operator, and Governance have different work views, and organization, property, and case provide further restrictions. According to the public platform description, a permission that has not been expressly defined is denied by default.
Oprivia is neither a locking system nor a camera platform, and it provides no legal authority to enter an accommodation. Creating a user account also does not verify the person's identity. Identity checks are separate features and are used only if they are technically active, contractually agreed, and legally permitted. Operators should confirm which roles, checks, and integrations are included in the current product version and agreement.
An initial review can begin with three questions. Can every key, code, and account be linked to a responsible person and a stated purpose? Will every permission end when the related stay, work order, or relationship ends? For sensitive access, can the record show who approved it and who used it? Each unanswered question points to a specific gap that the operator can address.
Sources and Notes
Editorial and professional context
Sources reviewed: September 10, 2026. The review combined Swiss data protection guidance, current platform policies, established models for access control, and Oprivia's published approach to permissions. The access inventory, seven-part context check, role assignments, and offboarding list are editorial recommendations for operational practice.
External professional sources
- NIST: Role-Based Access Control: users are assigned to roles, and permissions are assigned to those roles. NIST identifies the project page as archived and no longer updated.
- NIST: Least Privilege: guidance on restricting access to the minimum required for a task.
- ISO/IEC 27001:2022 and ISO/IEC 27002:2022: frameworks for information security management and security controls. Reference to these standards does not mean that Oprivia is certified or has implemented any particular control.
- Airbnb: Protecting your privacy: platform requirements concerning privacy, indoor cameras, and permission to enter during a reservation, subject to an emergency exception.
- Expedia Group: Guest Privacy & Host Entry Policy: the policy applicable to Vrbo bookings concerning emergencies and express advance consent for time-sensitive issues.
- Swiss Federal Data Protection and Information Commissioner: Video Surveillance by Private Individuals: guidance on the recording area, justification, proportionality, transparency, retention, access, and limits on evidentiary use.
- Swiss Federal Act on Data Protection: the Swiss legal framework governing processing principles, data security, and data-subject rights.
Oprivia sources
- Oprivia: Platform: four role views, access restricted by role, organization, property, and case, and default denial for undefined permissions.
- Oprivia: Governance: separation of duties, data minimization, approvals, escalations, and a continuous audit trail.
- Oprivia: Modules: responsibilities, tasks, evidence, review, and closure for operational cases and vendor work orders.
- Oprivia: Vacation Rental Vendors: additional guidance on entry tied to a work order, minimum disclosure of data, and verified closeout.
Scope and limitations
The right to enter an accommodation or view information depends on the stated purpose, the contract, relevant platform rules, and applicable law. Possession of a key or code, ownership of the property, and access to a user account may be insufficient to create the required permission. Rules governing surveillance, work, or tenancies can impose further limits. Oprivia is not a lock or surveillance system and does not replace professional security or legal advice. Identity checks and other functions depend on the current product version, agreed modules, and configuration.